


Introduction
This document presents a detailed post-mortem of the January 20, 2026 incident, which affected users with LP positions in the DUSD/USDC Curve pool.
This post explains the sequence of events between the time of the exploit and the publication of this post. It provides an analysis of the root cause and context on the escalation path of the vulnerability to the external liquidity pool. Lastly, a list of lessons learnt will be provided for posterity.
Executive Summary
On January 20th, 2026, at 03:40 UTC, an MEV searcher front-ran an exploit targeting the DUSD/USDC Curve pool, extracting approximately 1,299 ETH in profits.
The attacker manipulated the accounting mechanism for a Curve MIM-3CRV position held by the DUSD Machine, by using a flashloan to artificially inflate the MIM price. This inflated position value was then propagated to the Machine AUM, to the DUSD exchange rate and ultimately to the DUSD/USDC Curve pool through an external oracle. The attacker exploited this price dislocation by purchasing DUSD at fair value, inflating the oracle price, and then selling DUSD back at the inflated rate, repeating this process twice to drain the pool’s USDC.
Shortly after the exploit, the Security Council placed all three live Machines under Recovery Mode, for the time of the investigation. Importantly, no funds held inside the Machines were compromised, and the incident remained limited to LPs in the DUSD/USDC Curve pool.
The majority of extracted funds were subsequently recovered through coordinated onchain outreach, white-hat negotiations and cooperation from industry participants. Within a week, Makina implemented and deployed changes to harden accounting, completed the first batch of refunds to affected LPs, and safely restored protocol operations. This post-mortem details the full timeline, root cause, recovery actions and preventive measures implemented going forward.
Sequence of Events
All times in UTC
Incident detection & emergency steps
January 20, 2026
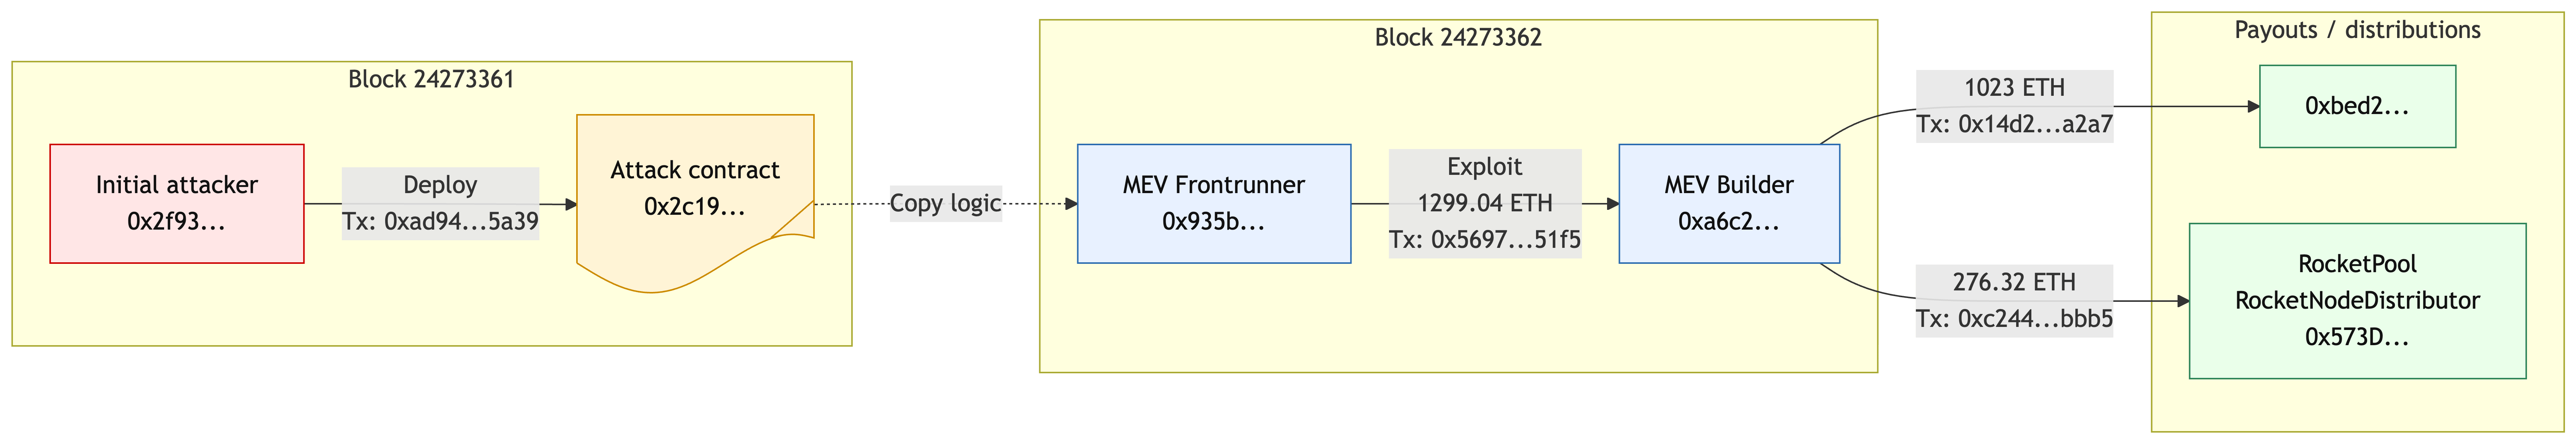
03:40:23 - The original attack contract is deployed at block #24273361 https://etherscan.io/tx/0xad945d38ec5dc00f0310b6f22d19da3b8b5063b9f3e7efb38ca6a5cbc6385a39
03:40:35 - The exploit transaction is executed. The original attacker is frontrun by an MEV searcher (0x935b) at block #24273362.
Net profits from the transaction are converted into 1299.17 ETH.
The MEV searcher keeps 0.13 ETH and the difference is sent to the block builder (0xa6c2) (1299.04 ETH):
https://etherscan.io/tx/0x569733b8016ef9418f0b6bde8c14224d9e759e79301499908ecbcd956a0651f5
The block builder sends 276.32 ETH to the block proposer, a Rocket Pool node operator:
https://etherscan.io/tx/0xc244aecf26d9f800179984d8bc747e2ab543f505d6da99bfbc0e098e302dbbb5
And 1023 ETH to 0xbed:
https://etherscan.io/tx/0x14d2725f4cac331740b053ae49176cec780b556e4aacc3a9f70d77644e97a2a7
03:40:35 - Makina team receives a Hypernative alert on exploit targeting DUSD/USDC Curve pool in block #24273362.
04:26 - Team becomes aware of the Exploit.
04:28 - SEAL911 establishes contact and opens a war-room with the Makina team, security researchers and auditors, the situation is assessed and remediation options are discussed.
05:29 - Quorum of Security Council multisig signers is reached.
05:46 - Security Council triggers Recovery Mode on DUSD Machine, exchange-rate updates, deposits, redemptions are paused:
https://etherscan.io/tx/0x69c504ce32a1df9d6302c1bbb937026eecb4488cef87420ce2a738b71966df45
06:04:11 - Security Council triggers Recovery Mode on DETH and DBIT machines, exchange-rate updates, deposits, redemptions are paused:
https://etherscan.io/tx/0x1d46ca565f38d39b58044200882c5efe6732fa7b8c1de1aa7b00586e5cdb34d4
Forensics, Tracing & Public Communication
06:42 - First communication on the incident published, asking Curve pool LPs to withdraw from the affected Curve pool:

06:45 - Tracing of the funds begin, the team acknowledges the exploit was front-run and ETH proceeds are held between MEV Block Builder and RocketPool’s reward contract.
09:26 - Onchain message sent to two addresses associated with MEV Builder holding 1,023 ETH or 78.7% of the extracted fund. Messages are also sent on Blockscan chat.
https://etherscan.io/tx/0xfe12d36617e2d1d6ab43716159ad7737606837fe9ea0cb781054f6f3c4fea52f
https://etherscan.io/tx/0xc5c5898eaf8c9ac7bee2c28eb971e8c5fee51c9ecdaf48b42c3357186c0235bf
~10:00 - Team talks with ChainSecurity, its primary security audit partner, to confirm the root-cause of the incident and discusses potential mitigation and security hardening approaches.
11:08 - Onchain message sent to address associated with RocketPool Validator holding 276.32 ETH or 21.3% of the extracted fund. Messages are also sent on Blockscan chat.
https://etherscan.io/tx/0xacffb5e680946cf0e7872271d465e8fa777f364a2027d5363efbcf70ff673177
13:36: Team informs legal counsel in all the relevant jurisdictions to initiate required steps.
13:28 - Security Council begins closing positions on DUSD/DETH/DBIT Machines:
https://etherscan.io/tx/0x90c6bc268b771b67031e75925767a4758e3f1f7e266b3034b4b85b019b484fff
13:30 onward - Team starts multiple workstreams: fund recovery & forensics, re-launch planning, smart contract upgrades, communications & daily community updates, coordination with LPs and external parties.
Recovery, Negotiation & Security Hardening Measures
January 21, 2026
The team continues throughout the day on the parallel workstreams.
10:00 - Team agrees on process and timeline for re-launch and starts working on required steps. Forensics and investigation continues.
14:00 - Meeting with ChainSecurity to discuss approach to smart contract hardening, agreement is reached on the path forward: make accounting optionally permissioned, add guards to machine exchange rate deviation.
14:30 - Implementation of contract changes begins.
15:23 - MEV Builder (0xbed) which holds majority of funds responds to messages on Blockscan chat, confirms assets are safe and commits to send back within 24h after address verification, and executes a test transaction.
https://etherscan.io/tx/0xef4db5a82f6cfb7349b072b4e957cb236b7e21185589404d2953a4052bdea4cb
15:47 - Makina verifies authenticity of onchain message on public X post from official account:
17:10 - Team sends 10.276 USDC to Kraken deposit address linked with RocketPool Validator to trigger an email notification, in an attempt to attract attention to onchain message:
https://etherscan.io/tx/0xce89d7b1e056984c897ee4d66eb788fe4e4def6e5e58aa413562211d587c6716
17:20 - Team sends additional onchain message address which last interacted with Kraken deposit address from previous step:
https://etherscan.io/tx/0x05a7bba99b2effdc77b99e8428f9656c1470176415dad291b68e76fb7a1e99d1
21:00 - Daily update is posted on X with summary of previous 24 hours, and initial timeline for re-launch:
~22:00 - New smart contract implementation with additional hardening is provided to ChainSecurity for security review.
January 22, 2026
10:00 - Team continues to work on all workstreams, focusing now on establishing contact with the RocketPool node operator to recover the rest of the exploit profits. Additionally the team starts designing the refund process and begins AML screening of target recipient addresses.
13:15 - 0xbed - the MEV Builder, sends back 920.7 ETH, keeping 10% bounty as defined in SafeHarbor policy:
https://etherscan.io/tx/0x0d23fea549bf8330cf47fabec75ad12b75cf0ade45cce68785067f2bda326a44
14:11 - Dedicated Recovery Safe is deployed, to isolate recovered funds from operational Safe:
https://etherscan.io/tx/0xdff982a048fdca0d4bd6ef9bf7b48ac216e8374ae7bf29f7f49ba93176132d98
14:44 - Recovered Funds are transferred to the recovery Safe:
https://etherscan.io/tx/0x52aabbeebb45d9eea8b7117b19a6f92300bfa1300cbd07b2a1087122eaec5b60
14:48 - Announcement about initial recovery made on X:
15:06 - Recovered ETH is wrapped to WETH to prepare for distribution:
https://etherscan.io/tx/0x673a83002017ce98bbbc5539147f9b24114e5baea45e963719bb100870527aa3
~16:00 - Outreach and coordination with liquidity providers to assist in providing secondary market liquidity to Machine Tokens once Recovery Mode is disabled for Machines.
17.45 - Contact is established with RocketPool validator through offchain communication channel. Agreement is reached to return the full share of funds the validator is eligible to.
18:00 - RocketPool team is contacted to establish feasibility of preventing 43% of the funds on validators being socialized to rETH holders.
January 23, 2026
10:00 - Agreement is reached with RocketPool team that it’s not feasible to prevent rETH distribution, as funds held on the validator contract are already accounted for in rETH backing.
Decision is made to move ahead with distribution, ensuring 157.1 ETH are recovered.
13:44 - RocketPool validator claims funds from validator contract:
https://etherscan.io/tx/0xd0c1836ee8e4562456d506872386086ab0f443735c58c80d6daed1775b7916fd
13:50 - RocketPool validator transfers 157.1 ETH to recovery safe address:
https://etherscan.io/tx/0x4e25dd868ff245424d3df25b835b68bff38df8ae0e38a071bf96022413704dd0
15:28 - ChainSecurity releases a provisional private audit report on updated smart contract implementation. [final version available here]
16:11 - Snapshot of balances of Curve LP tokens at the block of the exploit is published on GitHub, together with a python script for independent verification.
16:37 - New implementations are deployed for Makina V1.1, including the hardening changes as well as new features which had already been scheduled to go live on the 22nd of January
A full changelog of the upgrade can be found here:
17:10 - Remaining recovered ETH is wrapped to WETH to prepare for distribution:
https://etherscan.io/tx/0x155c441bd203276cec90bfb8d36f96a113603ed8c5d34cacb72e9cb49e2cdfd5
Restitution, Protocol Upgrade and Continued Investigations
17:15 - Communication goes out on X and Telegram with update on recovery status, refund and distribution process and next steps:
~18:11 - Allocations of refund amounts are computed for each user, addresses which profited from dislocation of the Curve pool after the exploit are excluded from refund.
18:49 - Batch transaction executed from Recovery Safe dispersing the recovered funds:
https://etherscan.io/tx/0xe95ec4316b81b06af9ed49ae5f73bafd544c5d909a99f726b1810cd936fd1a9b
https://etherscan.io/tx/0x18a5013c8b47bf05cc5e7f604d744c884ff5173e7ef3ab3eebd9e37094725c69
https://etherscan.io/tx/0x5cbf6bafefe84b6aedb0d30473e7d2c1658121e04adace93030cded97b7f2ba7
19:16 - Proxy upgrades for v1.1 implementations are set in timelock (24 hours):
https://etherscan.io/tx/0xf7f571ff0c356d541751caaf295d6892ea1fa5a5dc777998bec28b6e73662d85
January 24, 2026
~11:00 - Team shifts investigation into addresses with large profits from swaps in the dislocated Curve DUSD/USDC after the exploit, which took advantage of the situation to profit, causing further losses to LPs.
~12:00 - Team identifies an address with ~255,000 USDC in profits and a pending redemption request.
15:48 - Team contacts address owner to negotiate whitehat bounty in exchange for return of 90% of profits (229,963.24 USDC).
18:38 - Agreement is reached with the party in question to return 229,963.24 USDC after redemptions are re-opened and requests are settled.
January 25, 2026
~11:00 - Team continues investigation into address with large profits from swaps in the dislocated Curve DUSD/USDC.
~11:15 - Team identifies 0xddf6f217951a1e484ee6b04d621c861bf38d0656 as the wallet with the highest profits from swapping the DUSD/USDC after the exploit (513,994.89 USDC)
14:00 - Team works on restitution plan strategy.
16:00 - Blockscan Chat messages are sent to 0xddf6f217951a1e484ee6b04d621c861bf38d0656 and it’s funding wallet 0xce8a3b66c5509e7be0f65485f95b69159da870e4 (arbinomics.eth)
16:49 - Onchain messages sent to 0xddf6f217951a1e484ee6b04d621c861bf38d0656
https://etherscan.io/tx/0x0cfe8f9eb48bd885c4c1a2c927314e6adbb9871f4f66be5004f8ebde370ab60a
16:51 - Onchain messages sent to 0xce8a3b66c5509e7be0f65485f95b69159da870e4 (arbinomics.eth)
https://etherscan.io/tx/0x2f38df75e20a04946f728f0256f4be4b14a86ac2ff8298ef901059b176ef90bf
16:54 - Onchain messages sent to 0xc76DeF2FEc311D6d0F829Ec26a6bBF760Af2a2B6
https://etherscan.io/tx/0xacda151f45ee8492026d38d7f51bbae8d4a6d42fb538ead7607cb330305c4482
Recovery Mode Deactivation and Return to Normal Operations
January 26, 2026
09:19 - Operator returns 104,491 USDC, inadvertently earned by DUSD on volume generated by exploit on MIM/3CRV pool, to be included in recovery distribution to affected LPs
https://etherscan.io/tx/0xc0e30fb95502cdef9a2a37c33f4c8d67590d5d97ac56bb2ed91697457717a4d9
16:35 - Timelock transaction is triggered to upgrade contracts to v1.1 and including contract hardening changes:
https://etherscan.io/tx/0x14a98f38f3233e740b8b30413325d114d3f7ccedeee30f291943156986392262
16:36 - Permissioned accounting for all deployed machines is enabled, and selected keeper addresses are approved to run accounting:
https://etherscan.io/tx/0x2de76287a12a0c9fa60282a683b2a4e221ddc4526bd33ee16562886f4bbf718b
~18:00 - Coordination with external liquidity providers to reinstate liquidity allowing for secondary market swaps
18:07 - Security Council turns off Recovery Mode, re-enabling normal functioning of Machines, including settlement of redemptions:
https://etherscan.io/tx/0x0b5cae120bb2ebd527a6fdc3fae60da427a990cb61cf27336fc0c56243f801c6
~18:15 - Operator starts settling pending redemptions allowing users to claim.
After 18:15 - All machines operate normally again, users can redeem at the pre-exploit exchange rate, secondary market liquidity is available, investigation into high-profit addresses continues.
18:34 - Protocol upgrade announcement is published on X:
20:14 - Recovery and restitution strategy plan is announced on X:
Following days
The team continues its efforts to recover additional funds and starts designing the NFT based mechanism for future revenue share. The team maintains open communication lines with affected users, security firms and external liquidity providers.
Attention gradually returns to protocol growth, operator onboarding and development of new features and products.
Root Cause Analysis
Makina is designed to create robust and flexible infrastructure for onchain asset management. A key feature which enables this are Weiroll based scripts called Instructions.
Instructions are used to manage positions or account for them. Accounting Instructions are pre-approved executable Weiroll scripts that read onchain data and compute position values.
For a given strategy, each supported chain has an associated Caliber. The values of all positions managed by a Caliber are aggregated into that Caliber’s AUM. All Caliber AUMs for the strategy are then aggregated into the Machine AUM, from which the Exchange Rate is derived as ER = AUM / MT_Supply.
In the context of the strict scope of the Machines, the exchange rate is used to calculate amounts for deposits and redemptions. Deposits get priced atomically, whereas redemptions use a lower-of-two pricing, meaning they get settled at the lower price between when users request redemption and when the redemptions get settled.
In addition to these, oracles external to the Machine and to the Makina core protocol use the exchange rate for pricing in liquidity pools. Specifically the Curve pools for secondary market liquidity on Machine tokens, use an oracle to set the price in the pool, to better concentrate the liquidity in the pool around the “fair price” and minimize slippage to users.
The root cause of the exploit was an accounting instruction for the Curve MIM/3CRV used by the DUSD Machine to price the value of the corresponding position.
The instruction used the function calc_withdraw_one_coin() to compute how many 3CRV tokens would be received if the position were to be withdrawn one-sidedly.
The exploit involved the attacker taking a flash-loan and using it to manipulate the balance of the pool, such that calc_withdraw_one_coin() would return an inflated amount of 3CRV tokens, effectively leading the Caliber to account for the position at an inflated rate.
The inflated position value was then atomically propagated to the Caliber AUM, then to the Machine AUM and then to the Curve pool oracle, effectively skewing the price of DUSD against USDC in the pool.
This allowed the attacker to first purchase DUSD at fair value in the pool, then manipulate the position value for the MIM/3CRV pool to inflate the Caliber’s AUM, then propagate the manipulated value to the Machine AUM and into the DUSD/USDC Curve pool’s oracle, allowing the attacker to then sell the DUSD back to the pool at a much higher price, effectively withdrawing more USDC than what was initially spent. This was repeated 2 times in the exploit transaction to fully withdraw all the USDC in the pool.
There are a few points along the path which made the propagation possible:
Position value updates (via approved Accounting Instructions) were permissionlessly triggerable by design, which facilitated the inclusion of manipulated position values in the Caliber AUM.
The AUM of the Hub Caliber (i.e. the Caliber deployed on the same chain as the Machine) could be updated in the same block as the Machine AUM. This enabled a manipulated Caliber AUM to be atomically included into the Machine AUM, resulting in an inflated Machine AUM. The ability to perform both updates within a single block enabled the use of a flash loan to realize the full exploit, removing the need for high upfront capital.
The oracle used in the Curve pool synchronously derives the exchange rate from the current Machine state and relays the information “as is” to the pool which uses the provided value to price DUSD.
Point 1. and 2. were not critical issues in the context and scope of just the Machine, they would not on their own have caused losses to the DUSD Machine. This is due to the extra protection provided by the redemption contract’s exit pricing mechanism, where assets always leave the Machine at the minimum of the two prices between when the user entered and when the Operator settles the redemption, effectively preventing exits at a manipulated price.
The vulnerability became critical in the context of the external Curve pool which was using an oracle which directly and atomically relays the exchange rate of the Machine token. Thus the manipulation of the underlying position was able to be propagated by the attacker into the Curve pool’s internal pricing atomically.
Hardening and Prevention steps
As a preventive action all Curve integrations have been removed from the set of approved instructions, and an analysis was performed on all remaining integrations to assess their vulnerability to similar exploits.
Additionally, two changes were made (in commit #618b8f3) to the Makina core contracts to limit the impact of potentially manipulable instructions by strengthening controls over accounting and exchange rate derivation:
Optional permissioned accounting was introduced. If enabled, only a closed set of addresses are able to call the accounting functions, greatly reducing the risk of malicious external accounting. This feature would have prevented the attacker from being able to atomically propagate the manipulated position value to the Caliber’s AUM.
An exchange rate guard was added. This allows Risk Managers to set bounds for maximum deviation rate of the exchange rate. This effectively prevents the exchange rate from moving by an unreasonable amount in a short period of time, preventing any abnormal position values from propagating beyond the Machine to external protocols.
These changes have been included in the contract upgrade for Makina V1.1 (upgrade which was already scheduled to go live the week of the exploit).
Lessons Learned
The team has learned many lessons through the events that unfolded, we present a non-exhaustive set of lessons here for posterity:
Audit scope definition: Throughout the audit process, the analysis focused primarily on the core Makina systems, under the assumption that approved accounting instructions were non-manipulable. Within this threat model, the objective was to ensure that no funds could be extracted by the Operator or other malicious users. As a result, the downstream impact of potential accounting manipulation on external integrations was not a primary focus of the assessment.
Implication: Complex DeFi systems need to be assessed holistically, if a system is intended to be composable, all integrations to external protocols should be treated as part and in the scope of the security assessment.
Instruction review: While established procedures were adhered to, the sheer number of Instructions added during the initial root publication made the introduction of errors more likely, and the review process less focused.
Implication: Instruction reviews should focus on a smaller, related set of Instructions, and require a minimum of two independent reviewers by the Operator before submission to the Risk Manager, and subsequent review by the Security Council. More automated tooling should be introduced to identify potential issues earlier in the Instruction process.Recovery Process: Throughout the recovery process it became clear that speed is crucial, quickly sending on-chain messages to relevant parties, having forensics on all addresses to triangulate potential relationships and having a clear bounty framework as a basis for negotiation is what allowed to quickly recover and return funds
Implications: The available onchain forensics tooling is highly advanced and combined with deep research LLMs they are incredibly good at identifying relationships and connecting profiles to addresses. The SEAL SafeHarbor provides a framework to then negotiate with identified parties and reach agreement quickly.
Communications and Transparency: Having constant and transparent communications with the wider community was a crucial component to remove uncertainty and provide available information such that users quickly knew if they were affected or not and what the status of recovery and restitution is.
Implications: Over communication in crisis situations is important and crucial to inform and update affected and non-affected parties alike. Ensuring users have full information to make decisions.
We would like to express gratitude and thanks to the Makina community and users for showing patience while the team worked through this incident. Also, to all our industry partners and colleagues who have reached out with support and assistance during this challenging event.
Specifically we would like to once again thank: ChainSecurity, SEAL911, Flashbots and RocketPool teams, CyberFund, the MEV builder 0xbed, the RocketPool validator, and all the users who restituted their arbitrage profits.
These difficult situations show how the DeFi space can unite and strive towards the best outcome for everyone.
Hi, quick question.
What was the situation with HyperNative. It warned you about an exploit, but there wasn't any option for pausing protocol automatically?